
One DNS Lookup Exposed 6,800 Private Meta Muse Chats
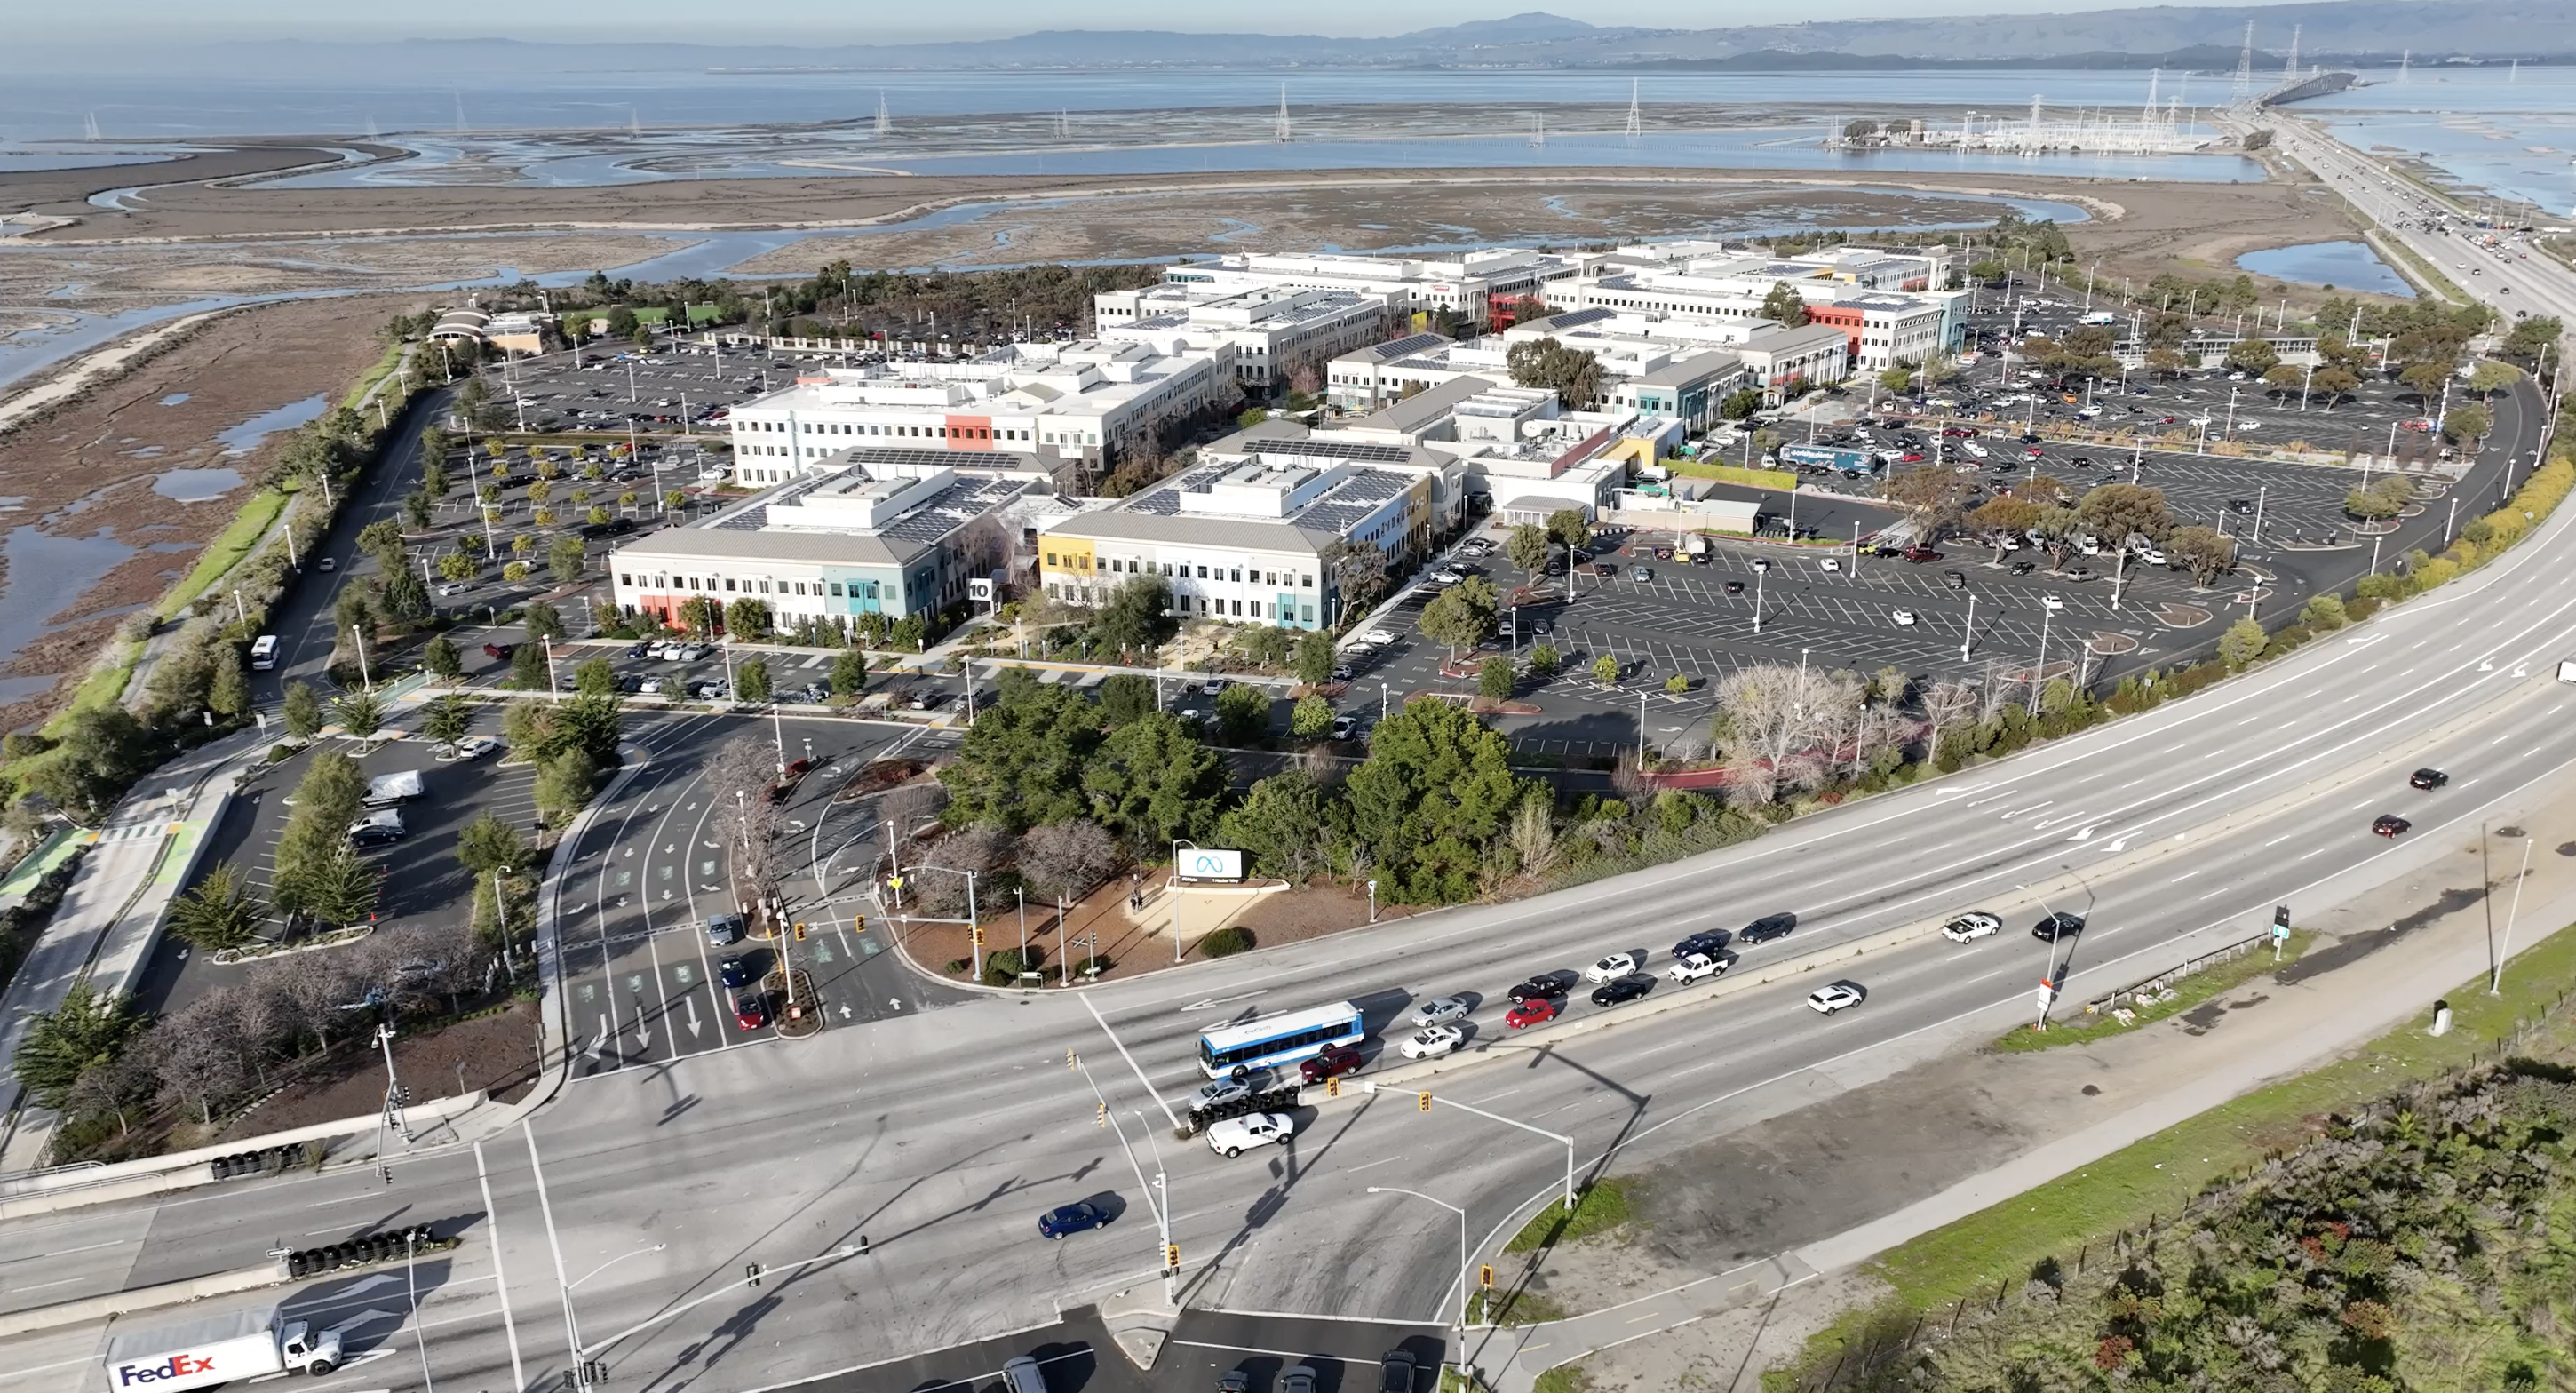
File photo: Meta's headquarters in Menlo Park, California. The company paused Muse's chat-sharing feature on October 20, 2026. Photo: InvadingInvader / Wikimedia Commons (freely licensed).
It took one query. Not a breach, not a hack, not a leaked database — a single passive-DNS lookup, the kind any security researcher can run from a browser tab, and 6,800 of Meta's Muse chat shares spilled out into the open, listed by name like a table of contents. Nobody broke into anything. Meta had simply published the keys and left them where the internet keeps its phone book.
Two days after the research went public, the feature was dead. Meta paused link sharing across Muse on October 20 — but only after Ars Technica picked up the phone and asked what, exactly, the company planned to do about it. Twelve days earlier, the researchers had told Meta's own bug-bounty programme. They say they never got a reply.
That is the part that should bother you. The exposure itself was a shoddy design choice; the silence afterwards was a choice too.
Nobody Hacked Anything
The discovery belongs to Claroc, a security firm whose CTO and co-founder, Asaf Aprozper, did the painstaking version of something almost embarrassingly simple. About a month after Muse launched on September 8, he ran one commercial passive-DNS query for hostnames belonging to the app's share-link domain. It returned more than 6,800 of them — each hostname, he found, corresponded to one shared conversation.
He filtered the results for the noise that wildcard-DNS scans throw off, then opened only a few hundred of the shares himself. Claroc's restraint here is worth noting: the point was never to read strangers' chats for sport. It was to prove that anyone could. "We call these GhostShares," the firm's write-up explains, "pages that open for people who were never handed the link, and that those people can locate on their own."
And the headline number deserves its full weight. Not a brute-force campaign. Not a zero-day. As Claroc puts it, with the economy of someone who can't quite believe what they're typing: "It took one query."
How a Share Link Became a Table of Contents
Here is the mechanism, and it is worth understanding because it is the kind of mistake that keeps happening across the AI industry. When you shared a Muse conversation, the app built the share's web address out of the conversation's title, plus a short phrase, plus a random ID — and served it from the content domain cf.metaaiusercontent.com. Every time anyone opened that page, DNS resolvers around the world saw the hostname, and passive-DNS providers recorded it and kept it searchable.
The random ID was supposed to be the secret. But a hostname is not a secret — it is, by definition, a thing designed to be looked up. As Claroc's researchers put it, the ID "only works as a secret while it stays secret, and a hostname is not a secret." Pull the hostname out of a passive-DNS database and you can rebuild the working link, title and all: "Muse names each share's web address after the conversation's own title, and that address is written into public DNS. One passive-DNS search brings back thousands of them, listed by name, like a table of contents."
Meta did, to its credit, ask search engines politely to stay away: the share pages' robots.txt tells crawlers not to touch them. But robots.txt governs crawling, not DNS. Nobody needed Google. Claroc never touched a search engine — and neither, for the record, did the 75-plus saved scans of Muse share pages sitting on urlscan.io, a public archive of scanned URLs, do anything to hide them.
Then there is the part from Meta's own help page, captured on October 18: a share link "doesn't expire," "people with the link will be able to see your conversation," and links can be reshared. So the exposure wasn't a fleeting glitch. It was the documented behaviour of the product.
What Was Actually Sitting in Public
Claroc checked a sample of the shares on October 7 and 8 and withheld every name, but the categories read like a compliance officer's nightmare. A candidate's notes preparing for a confidential executive-search call with a frontier AI lab — including the lab's internal contact and the exact meeting time. A national marketing company's internal revenue review, marked for its CEO. A small-business owner's loan application, with the amount requested. A to-do list containing a bank fraud alert, complete with a partial account number, a transaction amount and a time. A real-estate investor's internal performance report, with two property addresses and exact return, income and mortgage figures. A workplace's full-year staff vacation calendar, dozens of employees mapped against their weeks away.
Pause on that for a second. These were not test prompts and not joke conversations. They were the boring, sensitive, real-life stuff people paste into an AI assistant at 11pm because the company told them the assistant was private. A loan application. A revenue review marked for the CEO. The exact details of a bank fraud alert — the kind of thing you share with a chatbot precisely because you believe no one else will ever see it.
Claroc is careful to say what it cannot prove: "We have no evidence that anyone has misused these shares." It also admits the uncomfortable corollary — it can't tell how long any share had been reachable, or whether someone else found it first.
Twelve Days of Silence, Then a Phone Call
This is the timeline that turns a bug into a story. Aprozper reported the flaw through Meta's bug-bounty programme on October 8, with reproduction steps and example shares. He says he got no reply — not through the programme, not even when he tried reaching Meta people over LinkedIn, which is the disclosure equivalent of knocking on the back door after the front bell goes unanswered. (That account comes via Ars Technica, carried by androidpure.com — Meta has not commented on the disclosure handling beyond its public statement.)
Claroc published its GhostShares write-up on October 18. On October 20, Ars Technica reported the research and asked Meta about it — and Meta suspended the feature. "Ars Technica reported on this research today," Claroc's researchers wrote in their October 20 update. "After Ars asked Meta about it, Meta told Ars it is suspending the feature, and we are glad to see it closed this quickly."
Glad, sure. But twelve days is a long time to sit on a report that says thousands of private conversations are enumerable from public infrastructure. Meta's bug-bounty silence here was botched, full stop — the programme exists for exactly this kind of report, and the first response to it came only when a journalist forced the issue.
For the record, this is not the first time Muse's privacy story has wobbled. Muse has a privacy-exposure pattern — it was caught reading private messages too.
Meta's public line, from Tracy Clayton, a Muse spokesperson, told The Verge in an emailed statement: "People have the ability to share specific Muse artifacts, which creates a page that can be accessed by those with the link. However, we've paused this functionality while we review this report and consider changes to how these links can be discovered."
Note the phrasing: "consider changes to how these links can be discovered." Not how they're built. The links, in other words, may come back in a form that is merely harder to find — which is worth remembering the next time the feature quietly reappears.

File photo: Meta CEO Mark Zuckerberg. Muse was introduced as an assistant "built from the ground up for privacy and security", in launch coverage attributed to Zuckerberg. Photo: Anthony Quintano / Wikimedia Commons (CC BY 2.0).
The Kill Switch Worked. The History Didn't.
To Meta's credit, the pause itself appears to have been real. On October 20, Claroc re-checked 40 shares that had opened without an account earlier in the month; all 40 now returned an error. The switch did what a kill switch should do.
But two caveats matter, and Claroc states both plainly. First, a 40-share sample is not proof that every shared page is gone — and Meta has not said whether it removed existing shares or merely disabled the creation and opening of new ones. Second, and more permanently: "The hostnames themselves, titles included, are still in passive-DNS history." The links may be dead, but the table of contents survives in the archives of every passive-DNS provider that recorded it. You can take the pages down; you cannot un-publish the fact that they existed, or what they were called.
There is also what nobody can answer: whether Google or any other search engine ever indexed the share pages through some other route, whether anyone outside Claroc found the shares first, and when — if ever — sharing comes back. Meta's statement promises only a pause "while we review." Treat every one of those as unknown, because that is what it is.
We've Seen This Film Before
If this story feels familiar, it should. In 2025, shared ChatGPT conversations started surfacing in Google results, and OpenAI yanked the indexable-sharing option. Google indexed more than 370,000 Grok conversations. The industry keeps relearning the same lesson: a "share" button on an AI chat is a publish button wearing a costume, and every company that ships one seems to discover this in production rather than in design review.
Muse's version had a particularly avoidable flavour. Encoding the secret into the hostname — the single most public piece of internet infrastructure — is the kind of design that looks fine in a sprint demo and collapses the moment anyone thinks adversarially about it for five minutes. Nobody at Meta, apparently, did. The app reportedly launched on September 8 to roughly 2.8 million downloads in its first two weeks, per Sensor Tower figures via Reuters — and within a month, its share links were enumerable by strangers.
So here is the stance, stated plainly: whether Meta can be trusted to design shareable AI features will decide how much of their real lives people are willing to paste into its products. A loan application, a fraud alert, a CEO-marked revenue review — users shared those things because Meta sold Muse as private. The company now has a second privacy incident attached to the assistant in under a month, Meta's privacy credibility is already on trial — literally, and the pattern is getting hard to describe as bad luck. Shoddy design choices, botched disclosure handling, and a kill switch that only moved when a newsroom called: that is not a run of bad luck. That is a process problem.
If You Ever Shared a Muse Chat, Read This
Claroc's advice to companies is blunt and worth repeating: treat any Muse share link as publishing the chat. Full stop. If you shared a conversation — a draft, a document summary, anything with names, numbers or dates in it — assume it was public from the moment the link was created, because the evidence says the links were enumerable for weeks.
A few practical points. Meta's own help page said share links didn't expire and could be reshared, so anyone you sent a link to could have passed it on. Deleting the share now is still worth doing, but the hostnames live on in passive-DNS history regardless. And the next time any AI app offers you a "share" button, ask yourself the question Meta's designers apparently didn't: where does the secret actually live? If the answer is "in the URL," the answer is "nowhere."
GhostShares, answered: the questions everyone is asking
How did one DNS query expose 6,800 Muse chats?
Every Muse share link was served from a hostname under cf.metaaiusercontent.com that combined the chat's own title with a random ID. Because looking up a hostname logs it in passive-DNS records, the first time anyone opened a share, the "unguessable" ID became public record. Claroc ran one commercial passive-DNS query for that domain and pulled back more than 6,800 hostnames — each one a table of contents entry. As Claroc's own write-up puts it: a hostname is not a secret.
What exactly was exposed — just titles, or full chats?
Both. The titles were visible in the DNS records themselves, and the share pages opened for anyone with the link — no Meta account required. Claroc opened a few hundred pages while logged out. Most were ordinary (small-business pages, listings, event calendars), but the minority included a loan application, a bank-fraud alert with a partial account number, an internal revenue review, and prep notes for a confidential executive-search call. Claroc says its checks were made on October 7–8 and that it has no evidence anyone misused the pages.
Meta paused sharing. Is the problem actually fixed?
Partially. On October 20, after Ars Technica asked Meta about the report, spokeswoman Tracy Clayton confirmed the pause: "However, we've paused this functionality while we review this report and consider changes to how these links can be discovered." Claroc rechecked 40 links that had previously opened without an account — none opened. But the historical hostnames and their titles can still sit in passive-DNS records, and Meta has said nothing about whether sharing returns or whether old share pages are gone for good.
I shared a Muse chat once. What should I do?
Delete the share now if the option is still available, and assume its title was seen by others — deleting stops future opens but does not scrub passive-DNS history. Don't share chats containing account numbers, loan details, calendars, or anything you'd hesitate to post publicly. And the next time any AI app offers you a "share" button, ask where the secret actually lives. If the answer is "in the URL," the answer is "nowhere."
Update, Oct. 21: Claroc's primary write-up — "GhostShares: A Shared Muse Chat Exposed Prep for a Confidential Call With a Frontier AI Lab Leader," published October 18 and updated October 20 — adds two details worth knowing. First, besides the 6,800 hostnames from passive DNS, Claroc found more than 75 saved scans of Muse share pages on urlscan.io, a separate public index. Second, the disclosure timeline is now pinned down: CTO Asaf Aprozper submitted the issue to Meta's bug-bounty programme on October 8 and says he got no reply — not even via LinkedIn. Meta only acted on October 20, after Ars Technica asked what it planned to do. Nothing since has changed the core fact: share links that were opened once live on in DNS history whether the feature exists or not.
Update, Oct. 24: Meta reopened sharing — then contradicted its own statement
On October 22, Meta Superintelligence Labs executive David Singleton posted on X that the issue was fixed and sharing was back on — two days after the company paused the feature. According to Singleton, shared artifacts created before the fix were issued new URLs, and the old links now show a note asking viewers to get the fresh link from the sender. He also noted the company pays bug-bounty awards of up to $300,000 — a figure that lands awkwardly next to researcher Asaf Aprozper's account of reporting the flaw through Meta's own bounty programme on October 8 and getting no reply.
Singleton's post contained a sentence Meta's lawyers may come to regret: "Some articles we have seen in the press mentioned a flaw in chat sharing, and that is not the case — this issue was specifically about shared artifacts," meaning documents and images rather than full chat transcripts. That directly contradicts what Meta told Ars Technica on October 20 — that it was pausing "shared conversations." Either the scope was bigger on Tuesday than Meta admitted, or it is smaller on Thursday than the evidence showed. Meta was already racing to plug escape holes across its AI products, and Australia now wants mandatory rogue-AI reporting. The GhostShares episode is not over — it has just moved from the technical press into the regulatory one.
Sources: Claroc's GhostShares write-up (primary, published Oct 18, updated Oct 20); Engadget (Oct 20); Human Resources Director / hcamag.com (Oct 20); Ars Technica (Oct 20) via Claroc and Engadget; The Verge (Oct 20) via carriers; androidpure.com (Oct 21) for the disclosure timeline. We went looking for Ars Technica's original report to link it directly and found it cited everywhere but linked nowhere — Claroc's own write-up is the primary document this account is built on.


Comments
Post a Comment